 SOPHOS XG338000ZZPCAU XGS 3380 Security Appliance
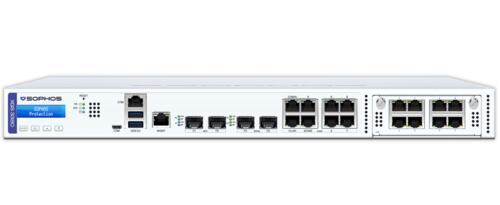
Next-gen firewall with 80 Gbps throughput, 25GbE connectivity
The Sophos XGS 3380 Security Appliance is a powerful, enterprise-grade next-generation firewall designed to deliver advanced cybersecurity, high-speed network connectivity and comprehensive threat protection for medium to large businesses, distributed organisations and demanding network environments. Featuring Sophos Xstream architecture, 80 Gbps firewall throughput, 32 Gbps threat protection performance and integrated 25 Gigabit Ethernet connectivity, the XGS 3380 provides the performance required to secure modern, high-bandwidth networks without unnecessarily compromising speed or productivity.
Powered by Sophos Firewall OS, the XGS 3380 combines sophisticated firewall capabilities, secure VPN connectivity, SD-WAN functionality and intelligent network traffic management in a compact 1U rackmount appliance. Its flexible security licensing allows organisations to start with essential firewall functionality and add Sophos Xstream Protection for advanced intrusion prevention, web filtering, zero-day threat detection, ransomware protection and centralised security management.
When combined with Sophos Endpoint Protection, Sophos XDR or Sophos Managed Detection and Response (MDR), the XGS 3380 also supports Sophos Synchronized Security, enabling network and endpoint security to share threat intelligence and coordinate automated responses to cyberattacks.
For New Zealand businesses, IT resellers and managed service providers, the Sophos XGS 3380 offers an attractive combination of next-generation firewall performance, 25GbE connectivity, hardware resilience and scalable protection against evolving cybersecurity threats.
Key Features and Benefits of the Sophos XGS 3380 Firewall
High-Performance Sophos Xstream Architecture
The Sophos XGS 3380 features a new single-CPU architecture with dedicated Xstream FastPath processing cores, designed to accelerate eligible network traffic while maintaining sophisticated security inspection.
Unlike traditional firewall designs that rely solely on general-purpose processing, the XGS 3380 uses dedicated processing resources to improve efficiency and handle demanding security workloads.
Firewall throughput
80 Gbps
Threat protection
32 Gbps
SSL/TLS inspection
9.5 Gbps
IPsec VPN throughput
74 Gbps
Manufacturer laboratory performance specifications. Actual throughput depends on traffic patterns, enabled inspection services and network configuration.
The XGS 3380 is particularly well suited to environments where large volumes of encrypted traffic, cloud applications, remote access connections and high-speed network services must be inspected and secured.
Integrated 25 Gigabit Ethernet and Multi-Gigabit Connectivity
The Sophos XGS 3380 includes a versatile selection of high-speed network interfaces, reducing the need for additional expansion modules.
Key connectivity features include:
- 8 × 2.5 Gigabit Ethernet RJ45 ports for high-speed copper connectivity.
- 2 × 10 Gigabit Ethernet SFP+ ports for fibre uplinks and network integration.
- 2 × 25 Gigabit Ethernet SFP28 ports for high-performance backbone and aggregation connections.
- 1 × Flexi Port expansion bay for additional network interfaces.
- Dedicated management and console connectivity.
The inclusion of 25GbE interfaces makes the XGS 3380 an attractive option for businesses upgrading to faster fibre internet connections, high-speed switching infrastructure and more demanding network environments.
Compact 1U Rackmount Design with Flexible Expansion
Despite its substantial processing capacity, the Sophos XGS 3380 uses a compact, short-depth 1U rackmount chassis, making it suitable for server rooms, network cabinets and distributed IT environments.
Its modular Flexi Port architecture allows organisations to add compatible interface modules as their network requirements evolve, providing flexibility for future expansion.
Improved Hardware Resilience and Serviceability
The Sophos XGS 3380 includes hardware features designed to improve operational reliability and simplify maintenance.
- Field-replaceable 256GB NVMe SSD: Allows the storage drive to be replaced through the Sophos RMA process without returning the complete firewall appliance.
- Optional redundant power supply: Supports installation of a second internal power supply to reduce the risk of disruption caused by a single power supply failure.
- High-availability support: Allows two compatible Sophos firewalls to be deployed in a high-availability configuration for improved business continuity.
The SSD is not hot-swappable, and replacement drives must be supplied through Sophos' authorised RMA process. The second power supply is optional rather than included as standard.
These features make the XGS 3380 suitable for business-critical network environments where reliability and maintainability are important considerations.
Sophos XGS 3380 Base Firewall Licence – What's Included?
Every Sophos XGS 3380 Security Appliance includes the Sophos Firewall Base Licence, providing essential firewall, networking and VPN capabilities without requiring an advanced security subscription.
The base licence provides the foundation for securing business networks and controlling how users, devices and applications communicate.
Core Firewall and Networking Features
- Stateful Firewall: Controls inbound and outbound network traffic using configurable firewall rules, network objects and access policies.
- Network Routing and Segmentation: Supports routing, VLANs and network zones to separate departments, users and critical business systems.
- Site-to-Site VPN: Establishes encrypted connections between offices, branches, data centres and remote locations.
- Remote Access VPN: Enables authorised employees and contractors to connect securely to business networks.
- SD-WAN Functionality: Supports WAN routing and traffic management to optimise connectivity across multiple internet services.
- High Availability: Supports active-passive and other eligible high-availability deployment options.
- Wireless and Firewall RED Functionality: Provides supported base wireless and RED capabilities, subject to compatible hardware and licensing conditions.
- Local Firewall Management and Reporting: Allows administrators to configure policies, monitor traffic and review local firewall logs and reports.
What Isn't Included in the Base Licence?
While the base licence delivers essential firewall and networking capabilities, advanced security features require additional subscriptions.
These include intrusion prevention, advanced web and application filtering, zero-day malware analysis, cloud DNS Protection, Sophos Security Heartbeat and advanced centralised reporting.
Sophos Central Firewall Management also requires an eligible paid security or support subscription.
Organisations requiring comprehensive protection against ransomware, malicious websites, network intrusions and sophisticated cyberattacks should consider upgrading to Sophos Xstream Protection.
Sophos Xstream Protection – Advanced Cybersecurity for the XGS 3380
Adding Sophos Xstream Protection transforms the XGS 3380 into a comprehensive next-generation security platform with multiple integrated layers of defence.
Xstream Protection combines Sophos' advanced network, web, zero-day and DNS security capabilities into a single subscription, simplifying licensing and administration.
What's Included with Xstream Protection?
|
Security feature |
Protection and benefits |
|
Network Protection |
Intrusion prevention, Sophos X-Ops threat intelligence, Security Heartbeat and advanced network security |
|
Web Protection |
Website filtering, application control and protection against web-based malware |
|
Zero-Day Protection |
Machine learning and sandbox analysis to identify unknown and emerging threats |
|
DNS Protection |
Cloud-based blocking of malicious and suspicious domains |
|
TLS Inspection |
Inspection capabilities for encrypted traffic to detect concealed threats |
|
Central Orchestration |
SD-WAN VPN orchestration and Central Firewall Reporting Advanced |
|
Active Threat Response |
Coordinated responses using supported Sophos and third-party threat intelligence |
|
Enhanced Support |
Access to Sophos' enhanced technical support and applicable support entitlements |
Advanced Intrusion Prevention and Network Threat Detection
Sophos Network Protection provides an advanced Intrusion Prevention System (IPS) designed to identify and block known exploits, malicious network activity and attempted attacks against vulnerable systems.
Combined with Sophos X-Ops threat intelligence, the firewall can respond to emerging threats and suspicious network behaviour, helping organisations reduce their exposure to cyberattacks.
Deep Packet Inspection and Encrypted Traffic Security
A growing proportion of business network traffic is encrypted, creating opportunities for attackers to conceal malicious activity within apparently legitimate connections.
Sophos Firewall supports deep packet inspection and SSL/TLS inspection, allowing organisations to identify threats hidden within encrypted traffic.
With up to 9.5 Gbps of published SSL/TLS inspection throughput, the XGS 3380 provides substantial inspection capacity for demanding business environments.
Zero-Day Malware and Ransomware Protection
Sophos Zero-Day Protection adds advanced analysis capabilities designed to identify malicious files and previously unknown threats.
Using machine learning, threat intelligence and sandbox-based analysis, suspicious files can be examined for malicious behaviour before they are allowed to compromise business systems.
This provides an additional defence against ransomware, advanced malware and threats that may not yet have established detection signatures.
Centralised Management with Sophos Central
With an eligible subscription, the XGS 3380 can be managed through Sophos Central, providing administrators and managed service providers with centralised visibility across multiple firewall deployments.
This simplifies security policy administration, monitoring, reporting and ongoing management for businesses operating multiple locations.
Sophos Synchronized Security – Connecting Firewall and Endpoint Protection
One of the major advantages of deploying a Sophos XGS 3380 is its ability to integrate with other Sophos security products through Sophos Synchronized Security.
Rather than operating as isolated security solutions, compatible Sophos products can exchange security information and coordinate their response to potential threats.
For example:
- Sophos Endpoint detects suspicious or malicious activity on a computer.
- Security Heartbeat communicates the endpoint's security status to the XGS 2380.
- The firewall can automatically restrict network access for the affected endpoint.
- Security teams can investigate and remediate the threat.
- Normal network access can be restored once the endpoint returns to a healthy security state.
This creates a more connected approach to cybersecurity, helping organisations detect attacks earlier, contain compromised devices and reduce the administrative burden on IT teams.
How Sophos Security Heartbeat Works
Sophos Security Heartbeat allows the XGS 3380 to communicate with compatible Sophos-protected endpoints and share information about their security status.
When a device becomes compromised, the firewall can automatically apply network restrictions based on configured security policies.
This coordinated approach can help prevent malware from spreading between computers, servers and other connected devices, while giving security teams more time to investigate and resolve the incident.
Why Combine Sophos XGS 3380 with Sophos Endpoint Protection?
A next-generation firewall provides critical protection at the network level, but many cyberattacks begin directly on computers, laptops and servers.
Phishing emails, malicious downloads, compromised credentials and infected applications can all introduce threats that bypass traditional network perimeter defences.
Adding Sophos Endpoint Protection extends security directly to individual devices, helping organisations protect against threats wherever users work.
Benefits of Combining Sophos Firewall and Sophos Endpoint
|
Sophos XGS Firewall |
Sophos Endpoint |
|
Protects network connections |
Protects computers and servers |
|
Inspects network traffic |
Detects malicious files and processes |
|
Blocks network-based threats with appropriate subscriptions |
Helps prevent ransomware and exploits |
|
Controls network and application access |
Monitors endpoint activity and security status |
|
Supports automated network containment |
Supports endpoint investigation and remediation |
When integrated through Sophos Synchronized Security, the two solutions provide a more coordinated security posture than either product operating independently.
Extending Protection with Sophos XDR and Sophos MDR
Organisations requiring greater security visibility and incident response capabilities can further strengthen their environment with Sophos Extended Detection and Response (XDR) or Sophos Managed Detection and Response (MDR).
Sophos XDR provides advanced investigation and threat detection capabilities, helping security teams correlate activity across supported endpoint, network, cloud and identity security sources.
Sophos MDR adds expert-led, managed threat monitoring, investigation and response, helping businesses detect and respond to sophisticated cyberattacks without maintaining a fully staffed internal security operations centre.
Combining Sophos Firewall, Endpoint and MDR can help organisations improve threat detection, accelerate incident response and reduce the potential impact of security incidents.
Sophos XGS Firewall Range – Hardware Comparison Chart
The Sophos XGS Series offers firewall appliances for small businesses, branch offices, medium-sized organisations and large enterprise networks.
The following comparison covers all 14 current XGS rackmount models, including the four new models introduced in November 2026.
Sophos XGS Rackmount Firewall Comparison
Throughput in Gbps. Fixed ports exclude dedicated management and console interfaces.
|
XGS model |
Chassis |
Fixed ports |
Flexi bays |
Firewall throughput |
Threat protection |
TLS inspection |
|
2100 |
1U |
10 |
1 |
30 |
5.6 |
2.0 |
|
2300 |
1U |
10 |
1 |
39 |
5.9 |
2.1 |
|
2380 (New) |
1U |
12 |
1 |
59.8 |
23.3 |
8.0 |
|
3100 |
1U |
12 |
1 |
47 |
8.3 |
3.2 |
|
3300 |
1U |
12 |
1 |
58 |
12 |
3.7 |
|
3380 (New) |
1U |
12 |
1 |
80 |
32 |
9.5 |
|
4300 |
1U |
12 |
2 |
75 |
28 |
9.0 |
|
4500 |
1U |
12 |
2 |
80 |
34.75 |
10.6 |
|
4580 (New) |
1U |
12 |
2 |
105 |
45 |
12 |
|
5580 (New) |
1U |
12 |
2 |
112.5 |
58 |
16 |
|
5500 |
2U |
16 |
3 |
110 |
46 |
13.5 |
|
6500 |
2U |
20 |
4 |
120 |
60 |
18.1 |
|
7500 |
2U |
22 |
4 |
160 |
70 |
19.5 |
|
8500 |
2U |
22 |
4 |
190 |
92.5 |
24 |
Comparison based on published November 2026 specifications. The new XGS 2380, 3380, 4580 and 5580 expand the existing range rather than directly replacing older models. Desktop XGS appliances are not included in this rackmount comparison.
Choosing the Right Sophos XGS Firewall
The Sophos XGS 3380 is particularly attractive for organisations requiring substantially greater threat inspection performance than the existing XGS 3300, without moving to a larger enterprise chassis.
Compared with the XGS 3300, the XGS 3380 offers:
- Approximately 167% higher published threat protection throughput.
- Approximately 157% higher SSL/TLS inspection throughput.
- Integrated 25GbE fibre connectivity.
- A compact short-depth 1U chassis.
- A field-replaceable SSD and optional internal power redundancy.
Organisations requiring additional Flexi Port expansion capacity, higher throughput or greater hardware redundancy may wish to consider the XGS 4580, XGS 5580 or larger 2U appliances.
Firewall selection should consider expected inspected traffic volumes, SSL/TLS inspection requirements, concurrent connections, VPN usage, interface speeds and future growth rather than headline firewall throughput alone.
Ideal Applications for the Sophos XGS 3380 Security Appliance
The Sophos XGS 3380 is designed for organisations that need high-performance security and flexible network connectivity.
- Medium to large businesses: Protecting business-critical applications, cloud services, servers and corporate networks.
- High-speed fibre networks: Supporting organisations deploying 10GbE and 25GbE network infrastructure.
- Multi-site organisations: Providing secure VPN connectivity and SD-WAN capabilities across offices and branch locations.
- Education and professional services: Supporting network segmentation, web security and application access policies.
- Managed service providers: Delivering centrally managed firewall and network security services to multiple business customers.
- Businesses upgrading older Sophos firewalls: Providing additional inspection capacity and modern connectivity.
- Organisations adopting Sophos Endpoint, XDR or MDR: Building an integrated security platform with coordinated threat detection and response.
Why Choose the Sophos XGS 3380?
The Sophos XGS 3380 Next-Generation Firewall delivers an excellent combination of high-speed connectivity, advanced cybersecurity capabilities, scalable licensing and hardware resilience.
With 80 Gbps firewall throughput, 32 Gbps threat protection performance, integrated 25 Gigabit Ethernet interfaces and a compact 1U design, the XGS 3380 provides a powerful foundation for protecting demanding business networks.
Whether deployed with the included Sophos Firewall Base Licence, upgraded with Sophos Xstream Protection or integrated with Sophos Endpoint and Sophos MDR, the XGS 3380 enables organisations to build a more comprehensive and coordinated cybersecurity strategy.
For New Zealand businesses, IT resellers and managed service providers, the Sophos XGS 3380 provides the performance, flexibility and security capabilities required to protect modern networks against evolving cyber threats.
Contact SnapperNet for Sophos XGS 3380 pricing, Xstream Protection subscriptions, licensing options and assistance selecting the most appropriate Sophos firewall for your customer's requirements.
